Recent Posts
Pages: [1] 2 3 ... 10
1
Quote
Shortly after this article was published, Google released another Chrome update that patches an actively exploited flaw in the V8 JavaScript engine, tracked as CVE-2026-85046.

Google rates the vulnerability as high severity and says an exploit already exists in the wild. An attacker could use a crafted HTML page to execute arbitrary code inside the Chrome sandbox. Because it is already being exploited, HKCERT rates the overall risk as extremely high.

After installing the latest update, Chrome should be at version 152.0.7977.82/.83 on Windows and Mac, or 152.0.7977.82 on Linux.

Chrome is rolling out an update for its desktop browser. The update includes 26 security fixes, two of which Google rates as critical use-after-free vulnerabilities.

How to update Chrome

If you don’t want to wait for the rollout to reach you, manually updating is easy.

The easiest option is to allow Chrome to update automatically. But you can end up lagging behind if you never close your browser or if something goes wrong with the update.

To update manually, click the More menu (three dots), then go to Settings > About Chrome. If an update is available, Chrome will start downloading it automatically. Restart Chrome to complete the update, and you’ll be protected against these vulnerabilities.

You can find an explanation of the version numbering system and step-by-step instructions in our guide: How to update Chrome on every operating system.

Technical details

Let’s look at the two critical vulnerabilities. Both are use-after-free (UAF) vulnerabilities. A use-after-free vulnerability occurs when a program attempts to access a memory location after it has been freed. That can cause crashes or, in some cases, allow an attacker to run their own code.

The first, tracked as CVE-2026-84353, was found in Shared Tab Groups and could allow a remote attacker using social engineering to execute arbitrary code outside the browser sandbox via a crafted HTML page. Here, social engineering likely means an attacker would have to lure you to a malicious website or open an email in HTML format.

The other critical vulnerability, tracked as CVE-2026-84352, was found in WebGL. WebGL, short for Web Graphics Library, is a browser technology that lets websites display interactive 2D and 3D graphics. The vulnerability could allow a remote attacker to execute arbitrary code outside the sandbox via a crafted HTML page.

Chrome vulnerabilities that enable remote code execution outside the browser sandbox are particularly valuable to attackers because they can turn a visit to a malicious or compromised website into direct code running on the underlying operating system, often without requiring additional exploitation steps.

source
2


We often write about important updates for the most popular browser, Google Chrome. Since it would be out of scope to post elaborate update instructions for every possible platform and operating system (OS)—like iOS, macOS, Windows, Android, etc.—we decided to turn this topic into a separate post that is easy to find (and link to). Also, keep in mind that not every update will be available for every platform or at the same time. You can find when the latest update for your operating system was released on this Google Chrome releases website.

Keeping your Google Chrome browser up to date is essential for security, performance, and access to the latest features. Whether you’re on Windows, Mac, Linux, Android, or iOS, updating Chrome is straightforward, if you know where to look.

But first a few words about the version numbers, because they can be confusing at times.

The Chrome version number consists of four parts separated by dots, like this:

MAJOR.MINOR.BUILD.PATCH

Each part has a specific meaning. In order of relevance they are:

MAJOR: This number increases with significant releases that may include major new features or changes. It usually raises in increments about 7 – 8 times per year, roughly every 6 weeks, reflecting Chrome’s release cycle.

MINOR: This number is typically zero and rarely changes. It mainly supports the versioning scheme but doesn’t usually affect how users track updates.

BUILD: This number increases steadily and represents a specific snapshot of Chrome’s source code at a given time. It advances with each new build candidate and is the key indicator of how recent the core code is.

PATCH: This number changes in increments for smaller fixes and security patches applied to a particular build. It resets with each new build and helps identify minor updates within the same build.

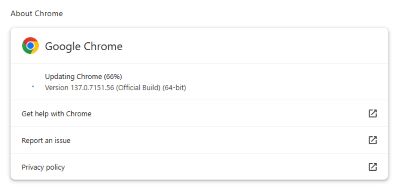
For example, a version like 137.0.7151.56 means:

   • Major version 137 (the milestone release)

   • Minor version 0 (standard)

   • Build number 7151 (the code snapshot)

   • Patch number 56 (the latest fix on that build)

Why does the version number matter?

The BUILD and PATCH numbers together uniquely identify the exact code you are running. Even if two versions share the same major number, a higher build or patch number means you have a newer, more up-to-date Chrome version.

Sometimes you might see slightly different patch numbers on the same major build, for example, 118.0.5993.117 vs. 118.0.5993.118. This usually happens because Google released a quick fix or minor patch shortly after the initial release. Both are part of the same major update, but the higher patch number is newer.

How to check if you have the latest version

To verify your Chrome version:

   1. Open Chrome.

   2. Click the three-dot menu (⋮) in the top-right corner.

   3. Go to Help > About Google Chrome.

Chrome will display your current version and automatically check for updates. If a newer version is available, it will download and prompt you to relaunch once it’s ready updating.


Chrome is updating

Update Chrome on Windows

Method 1: Use Chrome’s built-in update feature

   1. Open Chrome.

   2. Click the three-dot menu icon (⋮) in the top-right corner.

   3. Hover over Help, then click About Google Chrome.

   4. Chrome will automatically check for updates and download them if available.

   5. Once downloaded, click Relaunch to complete the update.

To enable automatic updates for Google Chrome on Windows, ensure that the “Automatically update Chrome for all users” option is enabled in Chrome’s settings. You can find this setting by going to “About Google Chrome” within the Chrome settings. Closing and restarting Chrome may be required to apply the update.

Method 2: using Windows Update (for Chrome Enterprise)

If your organization manages Chrome updates via Windows Update or group policies, updates may be automatic. Contact your IT admin if you don’t see updates.

Update Chrome on macOS

Method 1: For each device

   1. Open Chrome.

   2. Click the three-dot menu icon (⋮) at the top-right.

   3. Select Help > About Google Chrome.

   4. Chrome will check for updates and install them automatically.

   5. Click Relaunch to finish updating.

You can also set up automatic browser updates for all users of your computer if Google Chrome is installed in your Applications folder. Go to “About Google Chrome,” and click Automatically update Chrome for all users.

Method 2: For Chrome Enterprise

As a Mac administrator, you can use Google Software Update to manage Chrome browser and Chrome apps updates on your users’ Mac computers.

Update Chrome on Linux

Chrome updates on Linux depend on your distribution and how you installed it.

For Debian/Ubuntu-based systems:

   1. Open a terminal.

   2.Run:

Code: [Select]
sudo apt update
Code: [Select]
sudo apt --only-upgrade install google-chrome-stable
   3. Restart Chrome to apply updates.

For Fedora/openSUSE:

   1. Open a terminal.

   3. Run:

Code: [Select]
sudo dnf upgrade google-chrome-stable
3 Restart Chrome.

If you installed Chrome via a package manager, it should handle updates automatically when you update your system.

Update Chrome on Android

Chrome updates on Android are handled through the Google Play Store:

   1. Open the Google Play Store app.

   2. Tap your profile icon (top right).

   3. Select Manage apps & device.

   3. Under Updates available, look for Chrome.

   5. Tap Update next to Chrome if available.

Alternatively, if you have auto-updates enabled, Chrome updates automatically. To enable auto-updates for Android apps, open the Google Play Store, tap your profile picture, go to “Manage apps and device,” and then tap “Manage.” Select the app you want to update automatically, tap the “More” button, and toggle on “Enable auto-update.”

Update Chrome on iOS (iPhone and iPad)

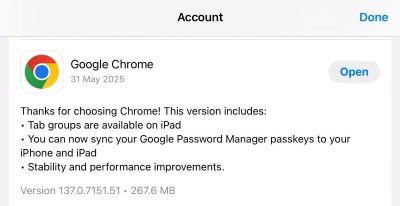
Chrome updates on iOS come through the Apple App Store:

   1. Open the App Store.

   2. Tap your profile icon at the top right.

   3. Scroll down to Available Updates.

   4. Find Google Chrome and tap Update.

If auto-updates are enabled on your device, Chrome updates automatically.


Chrome in App Store’s recently updated section

Updating Chrome on Chrome OS

Chrome OS updates include Chrome browser updates:

   1. Click the time in the bottom-right corner.

   2. Click the Settings gear icon.

   3. In the left menu, select About Chrome OS.

   4 .Click Check for updates.

   5. If an update is available, it will download and install automatically.

   6. Restart your Chromebook to complete the update.

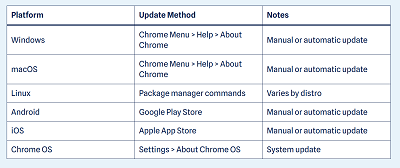
Summary table of update methods


source
3
IFA 2026 / IFA 2026: Microsoft confirms Windows 11 will boot faster and run on 8GB PCs
« Last post by javajolt on September 07, 2026, 02:26:19 PM »
But shares no numbers

At IFA 2026, Microsoft confirmed Windows 11 will boot faster, so you’ll notice the lock screen appear almost immediately. It also reaffirmed that Windows 11 will soon run well on 8GB RAM PCs, and even security features like Windows Hello will feel more responsive when the next big update rolls out.

Microsoft has spent much of 2026 promising that Windows 11 will get better at the things previous versions of Windows already excelled at, such as moving the taskbar, resizing the Start menu, or having more native apps. All of that was a normal part of the OS before Windows 11 happened, and Microsoft has finally realized it messed up.

Some of those promises have already come true, but if you haven’t seen any visible difference on your PC yet, it’s because of the gradual rollout. With the September 2026 Patch Tuesday update, scheduled for September 8, Microsoft will enable the movable taskbar, resizable Start menu, and let you remove Bing from Windows Search.

It’s a good list of improvements, but there’s more, and Microsoft teased some of it at the IFA 2026 conference.

Speaking at IFA 2026, Mark Linton, Corporate Vice President of Windows & Devices at Microsoft, confirmed that Windows 11 has already made significant gains in performance, and early internal benchmarks suggest the OS has reduced boot times.

“We’ve made significant gains on things like boot time, Windows Hello responsiveness…” Linton said.

Windows Latest understands that the faster boot time isn’t live in the preview builds, and Linton was likely referring to an internal build.

“We’re continuing to improve on the fundamentals,” Linton added. “We’re listening to customer feedback, continuously improving Windows, and you’ll see those updates as Windows just gets better as the updates come through.”

Microsoft wants Windows 11 to run well on 8GB of RAM

Microsoft has already suggested that it’ll make Windows run well on 8GB RAM PCs again due to rising memory costs, and we heard that statement again at IFA 2026.

“We’re optimizing so that 8 gig of RAM runs great on machines as well,” Linton said without sharing any numbers.

Nobody should be buying an 8GB RAM PC for any serious tasks, but that doesn’t mean Microsoft’s and the industry’s broader effort to make Windows or apps run better on 8GB of RAM is a bad idea.

It’s going to benefit everyone, including those with 16GB, 32GB, or more RAM. In fact, it’s good to see companies working to improve their software for a change, as that practice appears to have gone missing entirely over the last few years.

And if you don’t believe how unoptimized Windows apps are, just open Task Manager and stare at a few of the background processes, such as Discord, which, according to its own developers, can use up to 4GB of RAM. Or Microsoft Teams, which can use 1-2GB of RAM in an idle state.

For years, Microsoft has been pushing 16GB of RAM as the new baseline and 32GB RAM as the recommended hardware for the best gaming performance. Copilot+ PCs still have a baseline requirement of 16GB of RAM, so PCs that launched with 8GB of RAM do not qualify as Windows AI hardware, and that includes Microsoft’s own Surface laptop with 8GB RAM.

But the whole idea of pushing AI and justifying more RAM has backfired and contributed to rising prices. And Microsoft is now explicitly talking about optimizing Windows so that 8GB systems still “run great.”

source
4
IFA 2026 / IFA 2026: The 5 coolest phones I saw at IFA 2026 – including a new foldable
« Last post by javajolt on September 07, 2026, 02:17:53 PM »
There are many amazing devices at IFA 2026, but these five phones were the perfect combination of practical and fun design.


This year’s IFA show was filled with rollable laptops, weird robots and a particularly expensive Dyson toothbrush. However, being primarily a phone reporter, I was on the hunt for unorthodox smartphones –- particularly ones you can’t just get anywhere.

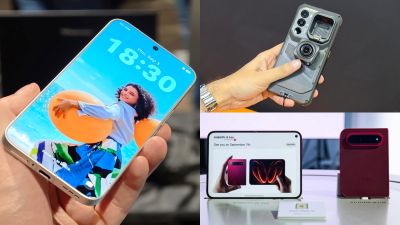
I stumbled across a new passport-size foldable, a zero-bezel phone, and one with a built-in action camera, among others. Here are the five coolest phones I saw at IFA 2026.

1. Xiaomi 18 Fold


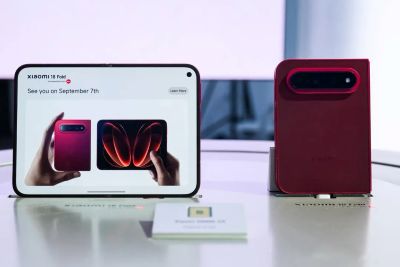
Xiaomi 18 Fold in Burgundy | Prakhar Khanna/ZDNET

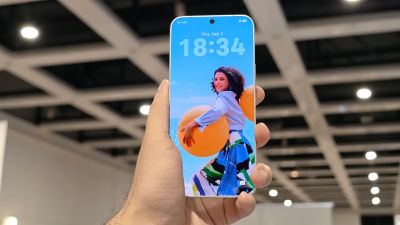
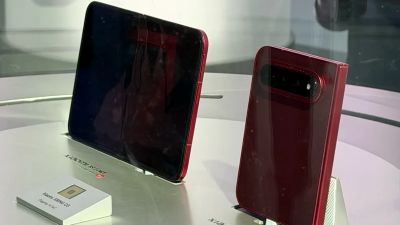
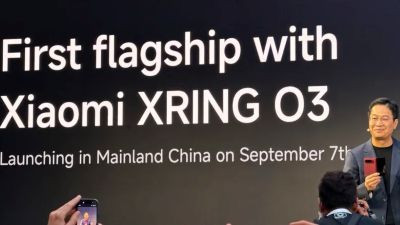
The Xiaomi 18 Fold is a Galaxy Z Fold 8-like passport-sized folding phone. Interestingly, it doesn’t have a Qualcomm or MediaTek processor, but an in-house XRing O3 chip; the first time Xiaomi is using its own processor on a flagship phone.

As for comparisons, the Xiaomi 18 Fold looks shorter than Samsung’s Galaxy Z Fold 8. On the back, it also has three cameras instead of than two.  The text on the camera bar suggests a focal range of 17mm-80mm, meaning it could have support for ~3.5x optical zoom.  We’ll need to wait for the September 7 launch for its full specs, but the less boxy design, rounded edges, and that burgundy color are already my favorite.

2. Tecno’s Bezelless concept phone


Tecno Next-Gen Bezelless Concept Phone | Prakhar Khanna/ZDNET

Tecno announced its Next-Gen Bezelless Concept Phone at IFA, and ss the name suggests, its display goes all the way to the edge, with no bezels. In my brief hands-on time, I used it to jump between apps, run the camera, and browse the web, and it felt very immersive. I was worried about the phone registering false touches from my palm, but it didn’t.

Also: Dell 14S first look: Taking on MacBook Neo… again

Tecno says this is only a concept phone and isn’t being mass-manufactured just yet. However, I wish we see at least one phone have a bezel-less screen next year. It looks futuristic, and I hope Tecno brings the design to more phones.

It also has a flowery 3D effect on the rear panel that looks gorgeous, and you don’t have to wear any sort of glasses to experience the effect. It was one of the most subtle but surprising things I’ve seen at IFA.

3. Motorola Razr 2026 Swarovski Edition


Motorola Razr 2026 Swarovski Edition | Ayano Tominaga/ZDNET

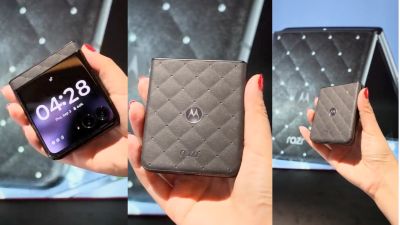
Motorola didn’t have a dedicated IFA booth, but the company announced its Swarovski edition Razr 2026 at the show. It has a quilted back in Pantone meteorite (black) color with Swarovski crystals embedded on top. These include 35 hand-positioned crystals and an additional 32-facet crystal on the hinge.

While the Razr 2026 retails for $800, its limited-edition Swarovski version is listed for 1,000 euros (~$1,160). Other than the looks, everything else remains the same as the regular model. However, the crystals give it a more luxurious look with that added quilted charm.

4. The RugOne XSnap 7 Pro’s detachable camera


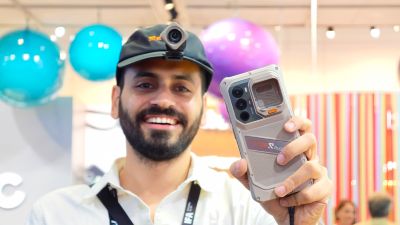
You can wear the detachable camera on your cap for PoV footage. | Prakhar Khanna/ZDNET

Rugged phone maker Ulephone’s sub-brand, RugOne, has a new smartphone with a detachable camera module. The RugOne XSnap 7 Pro holds a small action camera in the module that can be pulled out of the rear panel and mounted on your cap or a stand. This is potentially great for outdoor enthusiasts who don’t want to carry any extra gadget with them. The phone then doubles as a video-recording action camera.

It can capture 2.8K at 30fps or 1440p at up to 50fps, and you get two more (non-detachable) cameras on the phone:  a 50MP primary camera with OIS and a 64MP infrared night-vision camera paired with dedicated IR LEDs. It has a 6.67-inch display with a 120Hz refresh rate, 12GB of RAM with 512GB of storage and a huge 9,300mAh battery. The device will go on sale on Amazon and RugOne’s online store for $999 next month.

5. Oukitel’s rugged gaming phone


Oukitel WP600 | Prakhar Khanna/ZDNET

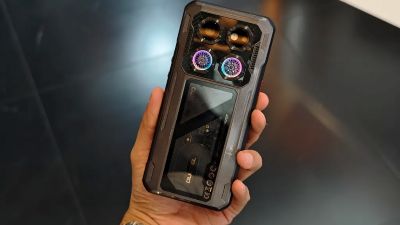
Rugged phones aren’t typically built for gaming, as all of their MIL-STD-level durability comes at the cost of processing prowess. You won’t find one of these phones powered by the same processor as a regular flagship phone, but Oukitel’s WP600 is pushes the limits with a MediaTek Dimensity 8300 chip. It isn’t a top-of-the-line processor, but the company claims it can deliver “exceptional speed and responsiveness for gaming, multitasking, and demanding outdoor applications.”

I couldn’t test the claims during my brief hands-on, but the Oukitel WP600 definitely feels built like a gaming phone. It has a ”cyber-futuristic aesthetic,” dynamic RGB lighting, and an integrated dual-fan cooling system to maximize the chip’s capabilities without toasting it.

You get a  6.8-inch FHD+ display with a 120Hz refresh rate, a 10,000mAh battery with 45W fast charging, 24GB of RAM alongside 1TB of storage and an MIL-STD-810H durability rating. It is a gaming phone built for outdoor enthusiasts.

source
5
IFA 2026 / IFA 2026: Xiaomi Showed Off 380 Products At IFA 2026
« Last post by javajolt on September 07, 2026, 02:01:45 PM »
But The One We Want To See Most Remains A Secret


For the longest time, Samsung has dominated IFA with one of the biggest booths in the trade show. In 2026, the South Korean company took a step back, as Chinese firms are now dominating the event. Among them, Xiaomi took over Berlin with over 3,300 square meters of exhibition space, bringing around 380 products to show off, including TVs, robot vacuums, humanoid robots, vehicles, smart home devices, accessories, and more. However, the one device everyone wants to try remains something of a secret: Xiaomi's upcoming Galaxy Z Fold 8-like foldable.

Locked behind thick glass, we know the device is called Xiaomi 18 Fold, it features a proprietary XRING O3 chip, and it's very red. With an official unveiling happening next week, ahead of Apple's long-rumored foldable iPhone reveal, Xiaomi is the latest company to attempt this new form factor.

While the device looks rounder than Samsung's counterpart, it's unclear how similar or different it will feel in hand during everyday usage. For me, a passport-like foldable phone seems to be the worst of mini phones and tablets combined. Still, this has been a format generating lots of attention, as Samsung has been selling more devices than it can produce. That said, even with Xiaomi keeping its phone behind glass, the company also focused on several other products for everyday customers, as it's now investing heavily in the European market.

Human x Car x Home is Xiaomi's strategy


"This year's IFA marks a significant milestone in Xiaomi's global journey," said Xu Fei, CMO of Xiaomi, during the company's IFA press conference. "Over the years, we have expanded from smartphones into smart home and smart vehicles, while investing deeply in foundational technologies, including AI." During the trade show, Xiaomi invited BGR to get a first look at the deep integration between its hundreds of products. In one of the sections, "AI Tomorrow," Xiaomi introduced a new hypercar concept, which wants to revolutionize the segment by combining comfort with fast speeds and a futuristic design.

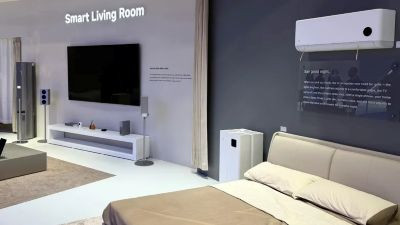
Even though the vehicle attracted plenty of attention, the real focus was the "AI Today" segment, showing the connection between current vehicles, smart living rooms, bedrooms, and more. For example, in a connected Xiaomi world, a customer would arrive home in their car. When leaving the car, the home's door would automatically be unlocked, the curtains would open, and lights would turn on. After finishing cooking and placing the dishes in the dishwasher, AI would know to start cleaning — including waking up a smart robot vacuum — without anyone saying a word.

Meanwhile, in the bedroom, as you'd lay down to read a book, the bed would automatically move to a more comfortable angle, the AC would turn on at your preferred temperature, and so on. According to Xiaomi, what's setting these experiences apart is the use of AI, which can predict what's next based on user behavior and a connected smart home app.

Understanding Xiaomi's AI models


Large language models and AI platforms like MiMo-V2.5-Pro, Xiaomi Miloco, and Xiaomi Miclaw are going to allow the company to deliver this AI-driven future. They allow the company's products to understand, reason, and take action. Like other brands, Xiaomi is integrating its LLMs with HyperOS and custom silicon architecture with the high-end XRING 03 chip that will power Xiaomi's upcoming foldable phone. This combination allows data to be processed locally and efficiently across smartphones, vehicles, and other connected home appliances.

With that, the system can synthesize multi-device inputs, interpret contextual cues like time (if you go to bed at a certain hour), geolocation (whether you're arriving or leaving home), and weather to deliver proactive assistance. Some options include the car preparing the climate control and lighting before the person arrives at home or printing a photo that has just been taken on the phone.

More importantly, these models are also key for the company's humanoid platforms like CyberOne, which handles real-world assembly tasks. This ongoing development forms part of Xiaomi's projected 24 billion euro R&D investment between 2026 and 2030, as the company wants to continue to bridge what AI intends to do and what it can actually do.

source
6
Nvidia's 616.86 hotfix fixes browser flickering, virtual displays, and Remote Desktop black screens.


Nvidia has released a new GeForce hotfix driver for Windows that addresses a handful of display-related problems, including browser flickering, broken virtual displays, and black screens in Remote Desktop sessions.

The new GeForce Hotfix Display Driver version 616.86 is based on the company’s latest Game Ready Driver 616.64 which brings DLSS 5, though there are some interesting hardware limitations that the new upscaling tech has managed to expose.

As is the nature of such emergency hotfixes, Nvidia says the release specifically targets three issues that have been affecting users following recent driver updates. First up, the hotfix resolves an intermittent flickering problem that could appear in web browsers when navigating to certain websites. The company has also fixed an issue where virtual displays could not be created after installing driver version 616.56. Another problem addressed by the release affects Remote Desktop Protocol (RDP) sessions. Nvidia says some users could encounter a black screen after updating to driver 616.56, and this should now be resolved with the new hotfix.

The full changelog is given below:

• Intermittent flicker may be observed in browsers when navigating to certain websites [6673430]

• Fixed an issue where virtual displays could not be created after updating to driver 616.56 [6674464]

• Remote Desktop Protocol (RDP) sessions may display a black screen after updating to driver 616.56 [6687328]

You can download GeForce Hotfix Display Driver 616.86 for Windows 10 and Windows 11 from this page on Nvidia’s support website. As always, if you don't have these issues, you can skip it. The fixes will eventually be rolled into a future official driver release, as they are cumulative.

source
7
DLSS 5 heavily increases RTX 5090 power demands, exposing 12V-2x6 connector and power-limit constraints.


The 12VHPWR connector burning / melting issue has been something pertinent to top-end Nvidia cards ever since the launch of of the RTX 40 series, and things have only gotten more and more common over time, so much so that, users have even started vibe-coding useful apps to monitor and restrict power in order to save their card from going up in flames.

Interestingly, it looks like there is another twist in the tale of the 12VHPWR connector, something that was discovered rather unexpectedly during testing of DLSS 5. If you have not been following, DLSS 5 is Nvidia's latest gen AI upscaling tech which was touted as the "GPT moment for graphics" during GTC 2026 announcement. As you are already familiar with, Nvidia is all-in on AI, and Jensen Huang just announced the purchase of Hugging Face earlier today.

However, DLSS 5 has been pretty divisive in the gaming community due to its nature of handling the rendering of upscalings. Regardless of the image quality and how they are cooked up, Tom's Hardware decided to put DLSS to a performance test using Nvidia's RTX 5090 Founders Edition (FE) along with MSI's RTX 5090 Lightning Z. The latter is a much beefier aftermarket variant because it packs two 12V-2x6 power connectors and can be configured with a massive 1000W power limit through its Extreme vBIOS. In essence, they were pitted against one another to see if DLSS 5 can actually make use of all that additional power headroom.

The testing involved running games at 4K with DLSS Performance mode, meaning the games were being rendered at 1080p natively before being upscaled. The maximum available rasterization and ray-tracing settings were used, with path tracing enabled in Cyberpunk 2077, though Multi Frame Generation (MFG) was left out so as to help isolate the performance impact of DLSS 5 only.

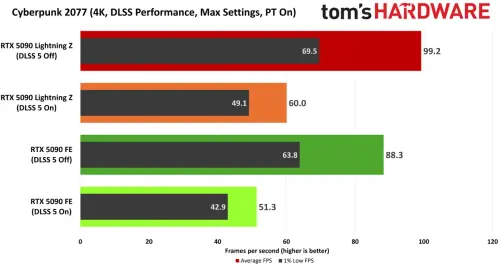
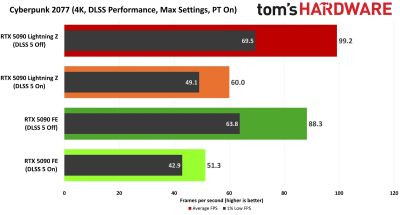
And the results were pretty interesting. In Cyberpunk 2077, enabling DLSS 5 caused the RTX 5090 FE to take a 42% performance hit, while the Lightning Z saw a slightly smaller 39% drop. However, the MSI card maintained a higher frame rate overall thanks to its additional power headroom.

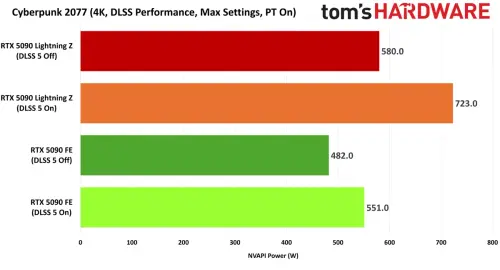
The power consumption numbers give an idea of what could really be happening. The Lightning Z went from around 580W to 723W with DLSS 5 enabled, which was a 25% increase. The FE, meanwhile, climbed from 482W to 551W, which is approximately 14.5%, but was effectively running into its power limit.

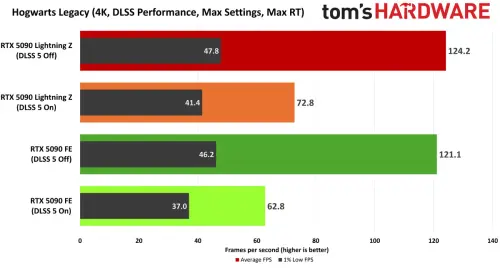
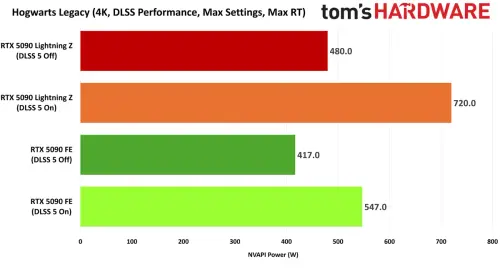
The same pattern appeared in Hogwarts Legacy as well where the Lightning Z's power usage jumped from roughly 480W to 720W, a staggering 50% increase. Performance also dropped by 42% on the MSI card, compared to 49% on the FE.

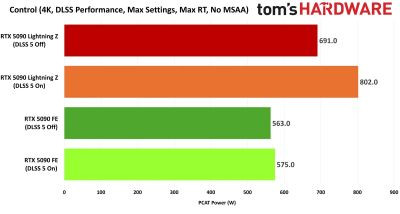
Control produced another interesting result. The Lightning Z was already consuming around 691W without DLSS 5, but that figure jumped to 802W with neural rendering enabled. The FE, on the other hand, once again ran into its 575W power limit. Despite both cards suffering a 42% performance reduction, the MSI model still managed 20% higher average frame rates thanks to its much higher power allowance.

This is where the 12V-2x6 connector becomes an unexpected problem for DLSS 5. The issue is not necessarily that the RTX 5090 cannot physically run the technology, but that Nvidia's Founders Edition design has a fairly hard ceiling on how much power it can provide through its single connector.

DLSS 5 appears to be really demanding on the Tensor Cores because its neural rendering system uses a diffusion-based AI model. Tom's Hardware's testing suggests that once you combine this workload with demanding ray tracing or path tracing, the 5090 can quite happily consume significantly more power than what the Founders Edition's 575W limit allows. This also implies that other low-cost AIB 5090 cards could put up similarly poor figures.

There is also an important caveat here, though. These tests were performed using community-made DLSS 5 mods that leaked earlier, instead than Nvidia's final implementation through its Streamline framework. Nvidia itself says the model takes around 8ms and 731 MB VRAM (via Nvidia Research) to process a 4K frame, and the performance seen through the mod was roughly in line with that figure, so the official implementation may not be dramatically different, though devs could still optimize it better for individual games.

Overall, the early testing suggests DLSS 5 is not exactly a free performance upgrade. Across the three games, the RTX 5090 experienced performance drops ranging from 39% to 49%, while the additional AI workload could push power consumption hundreds of watts higher on a card that has enough headroom to accommodate it.

gpus/]source[/size]
8
and the limits of the 12V-2x6 power connector may hold it back on the RTX 5090

A single 12V-2x6 plug might not deliver enough juice to let DLSS 5 run free.


It's been a wild few days for gamers, as a version of the DLSS 5 model leaked with NBA2K27 and promptly got modded into every game under the sun. After initial builds that relied on ReShade to make the model work, the community has since wrapped up DLSS 5 into an Optiscaler package that makes adding it to most games nearly painless. With that development, we wanted to get a sense of how the tech performs ahead of its official release.

We're not going to weigh in on the aesthetic or philosophical implications of applying DLSS 5 to a particular title here. That ground has been extremely well trodden already, and if you haven't been stuck under a rock this past week or so, you've likely seen what DLSS 5 can do for yourself.

We're more interested in getting an idea of the performance cost of getting DLSS 5 running, along with the power requirements it incurs. Whether you love or hate this model's effect on a game's appearance, you can weigh your feelings against the performance cost involved in getting there.

Before we get to the numbers, some caveats: the Optiscaler DLSS 5 injection method may not represent the behavior of this model when developers integrate it through Nvidia's Streamline framework. Streamline may offer less overhead and better performance than what we saw here.

But Nvidia's technical paper on DLSS 5 says that the model takes 8 ms to execute on a 4K frame, and that's essentially identical to the performance metrics that we saw from Optiscaler when it's running. So it seems unlikely that the official version will be far off the performance we measured if it's implemented in these titles using the proper channels.

For these limited tests, we chose to focus on the RTX 5090 Founders Edition's behavior under DLSS 5 to explore the largest performance drop one might expect from this community implementation of the tech.

Out of curiosity, we also grabbed MSI's RTX 5090 Lightning Z from the TH arsenal. This RTX 5090 has a unique two-12V-2x6 connector power setup and a 1000W power limit available through its Extreme vBIOS. Given the apparent arithmetic intensity of DLSS 5, we wanted to see whether running it would consume any of the extra available power headroom from that card's twin-plug design.

For our small sample of games, we used the following basic settings: a 4K output resolution target fed by DLSS Performance upscaling (i.e., a 1920x1080 input) without frame generation, as well as maximum raster and ray-tracing quality settings (or path tracing, in the case of Cyberpunk 2077) and DLSS Ray Reconstruction where it was available.

We didn't use Multi Frame Generation in these tests. We want to cleanly represent the performance baseline you can expect from DLSS 5 given the above constraints.


(Image credit: Future)

In exchange for those enhancements, the RTX 5090 Founders Edition takes a 42% hit from DLSS 5. Although the Lightning Z takes a slightly smaller 39% hit, its baseline performance is higher than the Founders Edition, so the MSI card maintains a 60 FPS average and much higher 1% lows than the single-connector card. That difference in smoothness is evident.


(Image credit: Future)

Part of that difference in performance comes down to power. As we noted, the RTX 5090 Lightning Z has a much larger 1000W power limit to play with, and it puts that headroom to use here.

The jump in power consumption from DLSS 5 on the Lightning Z is eye-popping: 580 W to 723 W, or a 25% increase. The RTX 5090 Founders Edition only goes from 482 W to 551 W, which means that it's practically power-limited.


Unlike Cyberpunk 2077, Hogwarts Legacy doesn't implement path tracing, but its extensive RT effects are still impressive. Importantly for our purposes, it's easy to get Optiscaler into this title.


(Image credit: Future)

Hogwarts exhibits the largest performance drop of these three games on the RTX 5090 FE, at 49%. The Lightning Z card drops just 42%, though, and its higher baseline performance makes for a smoother experience.


(Image credit: Future)

The Lightning Z once again illustrates just how much power DLSS 5 can pull if it's available, even in this "lighter" RT title. Without DLSS 5, the MSI card draws 480 W on average. With neural rendering enabled, it pulls 720 W, or a whopping 50% more power.


(Image credit: Future)

Finally, we tried the game that started the community DLSS 5 wave last week: 2019's Control. This early RT title still poses a stiff challenge for modern hardware if you crank its RT settings to the absolute max, as we did here.


(Image credit: Future)

The RTX 5090 Founders Edition takes another 42% hit to performance under these conditions, and the Lightning Z also drops 42%. But the higher power limits of the MSI card let it deliver 20% higher average frame rates and much higher 1% lows than the Founders Edition, and that's a smoothness boost you can really feel.


(Image credit: Future)

That extra performance does come at the expense of significantly higher power draw. The Lightning Z is already pulling a shocking 691 W without DLSS 5, but enable neural rendering, and it jumps to 802 W. The Founders Edition just runs into its 575 W power limit again.


At least in our experience with the community-made mod packages available so far, DLSS 5 has a large performance cost, similar to what we saw with ray tracing before the wide availability of DLSS: in the range of 39% to 49%, according to our small sample of results so far.

Official versions of DLSS 5 may perform better, but we won't know for sure until later this week. In any event, our observations of the behavior of the tech as implemented by the community match up with Nvidia's published guidance so far.

We don't expect vastly different or better performance from first-party implementations, although a developer's official DLSS 5 recipe could certainly look better in a given title than the current free-for-all with sliders that were never meant to be exposed to end users. We'll have to see what happens as developers take the time to tune DLSS 5 for their games as the tech makes its way into more titles through official channels.

Officially, DLSS 5 only supports RTX 50-series graphics cards, and if you're interested in running it with RT or PT, our results show that you're likely going to need to enable the full stack of Nvidia software tech available from Blackwell: DLSS Performance or Ultra Performance to achieve solid baseline frame rates, plus Multi Frame Generation for acceptable output fluidity.

Some have suggested that you don't need to run RT or PT alongside DLSS 5, but that doesn't make any sense at all given our experience thus far. Applying DLSS 5 to purely rasterized input does make it look better than it otherwise would, but it makes the higher-quality input of RT or PT titles look even better still. You definitely don't want to give up those advanced rendering techniques just because DLSS 5 exists.

But those software factors aren't the biggest hurdle that might affect DLSS 5's delivered performance, at least at the extremes. We were surprised to find that the RTX 5090 Founders Edition design is probably holding back the performance of DLSS 5 on that card, even with its 575W TGP. The Founders Edition was consistently at or near its power limit in our tests with neural rendering enabled, which tracks with the demonstrated evidence that, like other image generation models, DLSS 5 is extremely demanding of the Tensor Cores that power its underlying diffusion model.

The exotic MSI RTX 5090 Lightning Z and its 1000W power limit show that when it's stacked on top of ray tracing or path tracing, DLSS 5 can and will happily slurp down hundreds more watts than the Founders Edition—or any other RTX 5090 with a single power connector—is built to provide.

And when you pair that fact with its large performance cost on today's hardware, it's clear that DLSS 5 is a multi-generational technology built to take full advantage of graphics cards that don't exist yet, whether they're RTX 50 Super-series products with higher power limits or future GeForce products built with more advanced Tensor Cores on a newer silicon process node.

Even as it stands, the results we've seen from DLSS 5 so far in both official demos and in its rapid proliferation through community mods suggest that neural rendering techniques like this will mark a new epoch of photorealistic fidelity for real-time graphics and new generations of hardware that are better suited to running demanding AI models like this in real time.

It's an exciting new frontier out there, even if things feel a bit like the Wild West for DLSS 5 right now. Hold on to your hats.

source
9
Microsoft / Windows is a drop in Microsoft’s ocean, no wonder it’s been ignored
« Last post by javajolt on September 05, 2026, 12:08:13 PM »
While Azure and LinkedIn eat the profit


Why Microsoft ignored Windows for so long

I’ve written previously about the supposed realization in Microsoft that they need to pay more attention to Windows 11. To illustrate how Windows’ importance within the company has been overtaken, let’s look at some financial data.

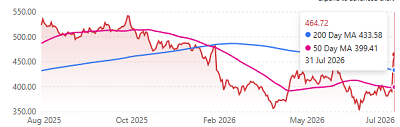
Microsoft published their latest fiscal year results, for the year ending June 2026. The numbers look very good if you’re a shareholder or investor – they beat estimates across the board, leading to a 16% rise in MSFT’s share price in one day, the largest ever one-day rise in stock market history (adding nearly half a trillion dollars to their market value). It was still $100 short of the peak in October 2025, when investors got spooked at Q1 FY26 fiscal results, the increasing capital expenditure on datacenters and slower uptake in Copilot usage.


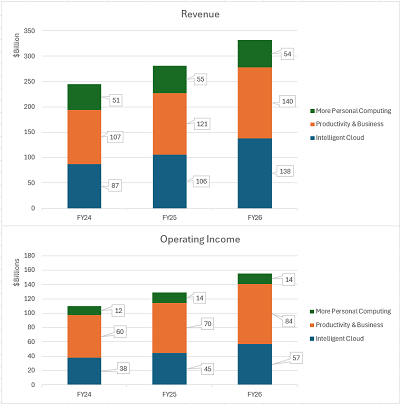
Microsoft has historically been vague at admitting where revenue is really coming in and how the cash is being spent with respect to individual products. Instead, they lump things together into categories like “Intelligent Cloud” (Azure, Github, servers – including Windows Server, and enterprise services). Windows client falls under “More Personal Computing”, which includes Surface devices and accessories, Xbox consoles and games/services and Bing/MSN advertising. These categories don’t exactly correspond to the corporate structure, i.e. there isn’t a “More Personal Computing” business unit per se, they’re just a convenient way for doing the financial reporting over the last few years.


It’s clear to see that “Productivity & Business” (which, alongside LinkedIn and Dynamics 365 includes Microsoft 365 services, apart from the revenue from Windows client licenses which are bundled in M365 but accounted for under More Personal Computing) is hugely successful, delivering the biggest slug of revenue and the highest profit.

For the last decade or more, Azure gets much of the attention inside Microsoft, and it makes up the biggest part of the Intelligent Cloud number; while it’s not broken out explicitly, Microsoft did say that Azure crossed the threshold of $100Bn in revenue this FY, meaning it’s the largest single product category in the company.

In FY26, More Personal Computing (MPC) delivered $54Bn in revenue, with an operating income of $14.4Bn. The revenue is down around $600M from the previous year but operating income is up $220M, so savings were being made somewhere or the mix of product was that higher-margin stuff was selling more.


Some analysts reckon Windows margin is 80%+, but if that $54Bn revenue is coming out at “only” $14.4Bn in income, the margin for everything that makes up MPC is more like 27%. That’s probably a lot of Surface hardware, Xbox Game Pass operating costs and a load more.

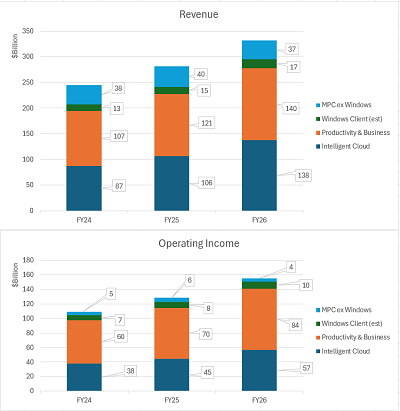
Commercial analysts have estimated that Windows client revenue accounts for a little more than 5% of Microsoft’s overall revenue; so for FY26 that might mean $17Bn in revenue and something like $10Bn of income. Still not too shabby.

But when you put the Windows revenue in context with everything else, it’s no wonder that Microsoft’s attention might have strayed from investing in what is a pretty stable and mature market, unless you consider ramming Copilot and other stuff in as “product improvement”.

If we make some estimates about the relative size of Windows within More Personal Computing and split them out, it’s clear that Windows is the largest part of that category’s profit, even if revenue from other parts of MPC is higher.


The total operating income from Windows is a drop in the ocean compared to everything else – Azure, even with all its datacenter capital expenditure and operating cost, probably brings in 4x the profit of Windows Client. LinkedIn on its own probably accounts for about $6Bn or $7Bn of income (and brought in nearly $20Bn in revenue).

If the Windows development team can focus more on quality, removing the unpopular advertising and unwanted AI stuff that’s been pushed in over the last couple of years, it may carry on being a multi-billion dollar profit center. It could even grow at double-digit %ages, which would be a dream scenario for many mature businesses. But it’s not going to be growing at 40% year on year, as Azure has been.


Any investment that Microsoft puts into making Windows 11 better must be seen as keeping existing users happy so they will continue to buy all the other stuff. As fans of Windows, we can only hope that it continues.

source
10
Passkeys were introduced with a strong security proposition. Replace passwords with public key cryptography, bind the credential to the legitimate service, keep the private key away from the server, and many of the phishing and credential theft attacks that have plagued enterprise security for decades become dramatically harder.

All of that is true. But the security conversation has changed very quickly.

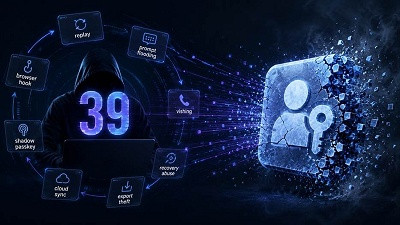
There are now at least 39 publicly documented methods, attack paths, research techniques, and exploitation scenarios involving passkeys and the infrastructure around them. Many already have working proof of concept tools or published research showing exactly how the techniques can be executed. Some are already appearing in real world attack patterns.

That does not mean criminals have operationalized all 39. It does mean the playbook is being written in public, and attackers no longer have to invent these techniques themselves.

More importantly, the research exposes a fundamental distinction that enterprises need to understand. The cryptography inside FIDO2 can remain completely intact while the account protected by the passkey is still compromised.

The Target Is No Longer Just the Passkey

A modern passkey authentication ceremony crosses an extraordinary number of trust boundaries. It can involve the web application, browser, operating system, password manager, cloud synchronization service, mobile device, Bluetooth transport, account recovery system, enrollment process, help desk, and ultimately the human being approving the authentication.

Researchers are attacking almost every one of those layers. Published techniques now include assertion mining, assertion replay, circuit breaker attacks, assertion phishing, browser hooking, assertion capture, challenge injection, detour replay, user verification manipulation, and user presence manipulation.

SpecterOps demonstrated the significance of this problem in its Pass the Passkey research. One of its most important observations was that malware does not necessarily need to extract a private key.

A malicious Windows application can ask the legitimate WebAuthn infrastructure to generate a signed assertion. The user sees what appears to be a legitimate Windows authentication experience, completes verification, and the attacker receives the resulting assertion.

The private key never left its protected location. The cryptography was not cracked. Yet the authentication process was successfully manipulated.

That distinction is central to understanding the new passkey threat model.

Even the Passkey Prompt Is an Attack Surface

Several of the 39 published techniques target the user interface surrounding authentication.

Researchers have demonstrated passkey prompt flooding, credential interface deception, application metadata spoofing, window handle spoofing, remote desktop passkey phishing, and FIDO interface overlay attacks.

This recreates a problem the security industry already encountered with push-based MFA. Users become accustomed to authentication prompts. Once authentication becomes a routine visual interaction, attackers can manufacture, repeat, disguise, or strategically time those interactions.

SpecterOps demonstrated tooling capable of repeatedly invoking legitimate looking Windows passkey prompts. Researchers also demonstrated techniques that can make malicious authentication activity appear to originate from an application the employee already trusts.

The lesson is important. Phishing resistance at the cryptographic protocol layer does not guarantee deception resistance across the operating system, browser, application, and user interface layers surrounding that protocol.

Shareable Passkeys Expand the Attack Surface

The attack surface grows significantly when passkeys can be shared, synchronized, exported, restored, or moved between devices.

The published inventory now includes synced vault compromise, Apple or Google account takeover, cloud recovery takeover, stolen or compromised phones, mobile malware, rooted mobile devices, hybrid authentication manipulation, KeePassXC export theft, Bitwarden export theft, credential exchange theft, malicious browser extensions, and attacks involving CTAP and Bluetooth communication.

This is not fundamentally a cryptography problem. It is an architectural problem.

Once a credential can move between devices, synchronize through a cloud account, be exported from a vault, be restored using another identity, or be recovered through another process, the security boundary expands far beyond the original authenticator.

An attacker no longer needs to defeat FIDO2. The attacker needs to compromise one sufficiently trusted component somewhere in the surrounding ecosystem.

A synchronized passkey can therefore use extremely strong cryptography while still inheriting the weaknesses of the phone, operating system, password manager, cloud account, browser, recovery process, and synchronization system responsible for managing it.

Enrollment and Recovery Create Another Opening

Some of the most consequential attacks do not steal an existing passkey at all. They simply create another one.

Published techniques include shadow passkeys, enrollment vishing, attacker phone enrollment, attacker controlled passkey registration, help desk takeover, temporary credential abuse, SIM based recovery, reverse vishing, and migration pretext attacks.

Consider what happens when an attacker gains enough control of an employee account to initiate legitimate passkey registration. Instead of extracting the employee's existing credential, the attacker registers an entirely new credential on a device controlled by the attacker.

Nothing has been cracked. Nothing has necessarily been stolen from the existing authenticator. The legitimate service itself creates a perfectly valid credential for the adversary.

This leads to an increasingly important identity principle. Phishing resistant authentication is insufficient if enrollment, replacement, recovery, and device registration are not protected to the same standard.

Dedicated Biometric Hardware Changes the Attack Surface

Dedicated biometric hardware approaches the problem very differently from passkeys stored on general purpose devices.

A purpose-built biometric authenticator can retain the private credential inside secure hardware with no cloud synchronization, no export mechanism, and no password manager responsible for moving the credential between devices.

Authentication can require a live fingerprint directly on the authenticator as well as physical proximity to the endpoint requesting access.

Just as importantly, a dedicated authenticator does not need to contain a traditional general-purpose operating system, an application store, a browser, or a screen.

That distinction eliminates enormous portions of the attack surface.

There are no third-party applications for an attacker to replace with malicious versions. Rogue applications cannot simply be installed on the authenticator. There is no browser extension ecosystem to compromise. There is no screen on which malware can present a deceptive authentication interface.

There is no consumer operating system filled with unrelated applications, permissions, background services, and update dependencies.

The authenticator performs a very small number of security specific functions and nothing else.

This drastically changes the economics of attacking it. Instead of attempting to compromise a huge general purpose computing environment, an attacker is confronting a tightly controlled hardware device designed specifically to protect cryptographic credentials and verify biometric identity.

It also makes the authentication process far more resistant to employee manipulation. An employee can be persuaded to visit a website, answer a telephone call, or follow instructions from someone claiming to be technical support. But social engineering cannot install a rogue application onto hardware that does not run ordinary applications.

It cannot manipulate a screen that does not exist. It cannot synchronize a credential through a cloud service that the authenticator does not use.

In that sense, properly designed dedicated biometric hardware becomes both highly resistant to attackers and highly resistant to mistakes made by employees.

Correct Service Configuration Is Critical

Dedicated hardware alone is not enough. The relying service must be configured to preserve the security model.

For sensitive enterprise environments, authentication and enrollment should be restricted to approved authenticator classes. The relying party should validate authenticator identity, enforce user verification, properly validate challenges and sessions, use appropriate signature counter protections, and prevent weaker methods from becoming fallback authentication paths.

Enrollment and recovery deserve particular attention. Adding a new authenticator should require proof from an already authorized authenticator rather than merely proving control of an account through a weaker recovery channel.

Configured correctly, this architecture prevents an attacker from simply enrolling an ordinary passkey from another laptop, phone, software vault, or security key. Cloud account takeover does not yield the credential. Password manager compromise does not yield it. Mobile malware cannot infect the authenticator.

A malicious application cannot be installed on it. And a remote attacker cannot manufacture the combination of dedicated hardware, biometric verification, physical proximity, and legitimate service interaction required to authenticate.

What the 39 Attacks Really Tell Us

The existence of 39 published attack methods does not mean FIDO2 cryptography failed. In many ways, it demonstrates the opposite.

Researchers repeatedly attack the software, synchronization systems, enrollment processes, operating systems, browsers, recovery mechanisms, and people surrounding the credential because defeating properly implemented cryptographic hardware directly is considerably more difficult.

That should tell security leaders where the next identity boundary needs to be.

For high value enterprise identities, credentials should not be freely shareable across consumer devices and cloud ecosystems. They should be bound to dedicated biometric hardware, the verified individual, the legitimate service, and an enterprise controlled enrollment and recovery process.

Passkeys solved a large part of the password problem. The 39 published attacks show us what attackers are targeting.

Dedicated biometric hardware, correctly implemented from enrollment through authentication and recovery, removes virtually all of that surrounding attack surface before an attacker ever gets the opportunity to use it.

Download the Token passkey security ebook to explore many published attack methods and see how dedicated biometric hardware changes the enterprise identity trust model.

source
Pages: [1] 2 3 ... 10